

Check Point warns of 48% rise in cyber attacks worldwide
Mon, 12th Oct 2026 (Today)
Organisations worldwide faced an average of 2,803 cyber attacks a week in September, according to Check Point Research. That was up 48% from a year earlier.
Its monthly threat data also showed a 16% rise from August, alongside increases in phishing activity, ransomware incidents and the exposure of sensitive information through enterprise use of generative artificial intelligence tools.
Education remained the most targeted sector, with 6,656 weekly attacks per organisation. That was 59% higher than a year earlier and 24% above August levels.
Telecommunications ranked second, with 3,483 weekly attacks per organisation, followed by government at 3,443. The figures suggest continued pressure on sectors with large user bases and complex digital systems.
Regional patterns
Latin America recorded the highest regional attack volume, at 3,813 weekly attacks per organisation, up 35% year on year. Africa followed with 3,701, ahead of Asia-Pacific on 3,593.
Europe recorded the fastest annual growth rate, with attacks up 61% from the same month in 2025. North America rose 50% over the same period.
The data also pointed to growing risks linked to workplace use of generative AI. One in every 39 enterprise GenAI prompts posed a high risk of sensitive data leakage, and 89% of organisations that regularly used the tools were affected.
A further 14% of prompts contained potentially sensitive information. The average user generated 131 GenAI prompts during the month, while organisations used an average of eight tools each.
Network and IT infrastructure data appeared in GenAI prompts at 71% of organisations, followed by financial data at 70%, legal and regulatory data at 68%, employee and HR data at 62%, and personally identifiable information at 60%.
By sector, business services recorded the highest high-risk GenAI prompt exposure rate at 4.9%, or one in every 20 prompts. Financial services followed at 4.1%, with healthcare and medical at 3.5%.
Latin America also had the highest regional rate of high-risk GenAI prompts, at 4%, above the global average of 2.5%.
Email threats
Email remained a major attack route. One in every 91 emails, or 1.1%, was classified as phishing in September, compared with one in 112, or 0.89%, in August.
Among phishing emails, 81% contained links and 11% contained attachments, making malicious links the main delivery method in email-based threats during the month.
North America recorded the highest regional phishing rate at 1.26%, or one in 79 emails. By industry, associations and nonprofits had the highest rate at 2.17%, followed by construction and engineering at 2.05% and real estate, rentals and leasing at 1.38%.
Ransomware rise
Reported ransomware attacks reached 824 in September, a 53% increase from a year earlier. Business services accounted for 31.3% of reported victims, followed by consumer goods and services at 15.2% and industrial manufacturing at 11%.
North America accounted for 46% of reported ransomware incidents, ahead of Europe on 25% and Asia-Pacific on 17%.
The Gentlemen was the most prevalent ransomware group in the data, accounting for 13% of published attacks. Qilin followed on 9%, while Akira accounted for 5%.
An additional 80 extortion groups also reported ransomware attacks during the month, indicating a crowded and shifting landscape beyond the leading operators.
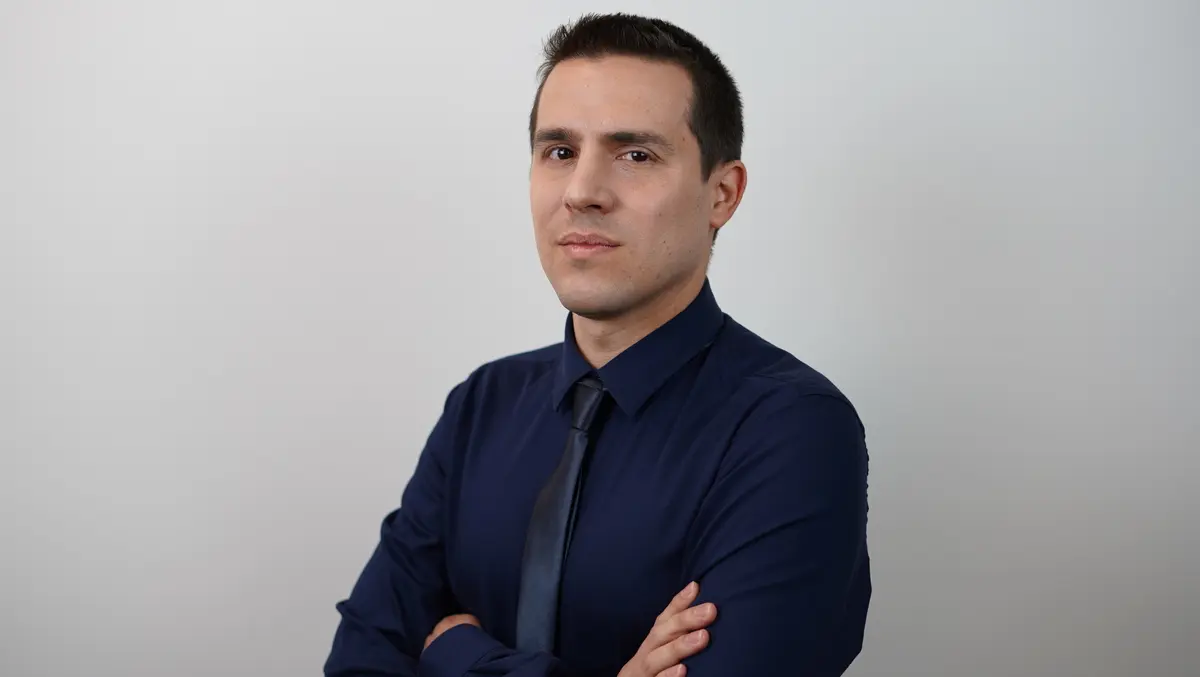
Omer Dembinsky, Data Research Manager at Check Point Research, said the figures showed pressure increasing across several fronts at once.
"September's data shows cyber risk increasing in both volume and breadth," said Omer Dembinsky, Data Research Manager at Check Point Research. "With attacks rising across every region, phishing becoming more frequent, ransomware remaining elevated and GenAI use expanding alongside sensitive data exposure, security teams cannot rely on fragmented defences. They need prevention-first protection that combines visibility, control and automation across network, cloud, endpoint, email and AI usage to stop threats before they disrupt operations or expose sensitive information."