
Securonix launches behavioural analytics for AI agents
Mon, 26th Oct 2026 (Today)
Securonix has launched Advanced Behavioural Analytics for security teams. The offering is designed to detect abnormal but permitted activity involving both human users and AI agents.
It combines Agent and Entity Behaviour Analytics with User and Entity Behaviour Analytics to flag patterns that may look legitimate when viewed as isolated events. Securonix says the system is intended to help analysts identify cases such as compromised accounts, insider activity and unusual AI agent behaviour by linking identity, authority, data use, asset sensitivity, timing and wider threat context.
Agent and Entity Behaviour Analytics, or AEBA, is aimed at enterprise AI agents. It is designed to identify when an AI agent uses an unexpected tool, accesses data outside its stated purpose or changes its normal operating pattern.
User and Entity Behaviour Analytics, or UEBA, focuses on people, identities, assets and systems. Securonix says it can connect signs such as unusual login times, growing data access and interactions with sensitive assets across multiple systems over time.
The combined approach is intended to help analysts investigate emerging risks rather than process separate alerts in isolation. Policies, approvals and audit records remain visible through detection, investigation, case management and response.
Security operations is the immediate target market. Securonix argues that traditional security information and event management platforms were built before enterprise AI agents became part of the attack surface, and that behavioural baselines now need to extend across users, identities, assets, applications, cloud environments and AI agents.
Within that framework, the technology correlates signals over time to identify compromised identities, unusual access, misuse of privileges, exposure of sensitive data and abnormal agent activity. Securonix also highlighted a growing catalogue of AI threat policies intended to detect techniques linked to AI-assisted reconnaissance, exploit development, privilege escalation and data movement.
A second part of the announcement focused on automation inside the security operations centre. Securonix said its AI SOC Analyst, called Sam, handles repeatable Tier 1 and Tier 2 tasks including triage, investigation, evidence collection and case creation, while its Agentic Mesh coordinates AI-supported workflows and Agentic Guardrails constrain actions within policy. Analysts must still approve consequential response actions.
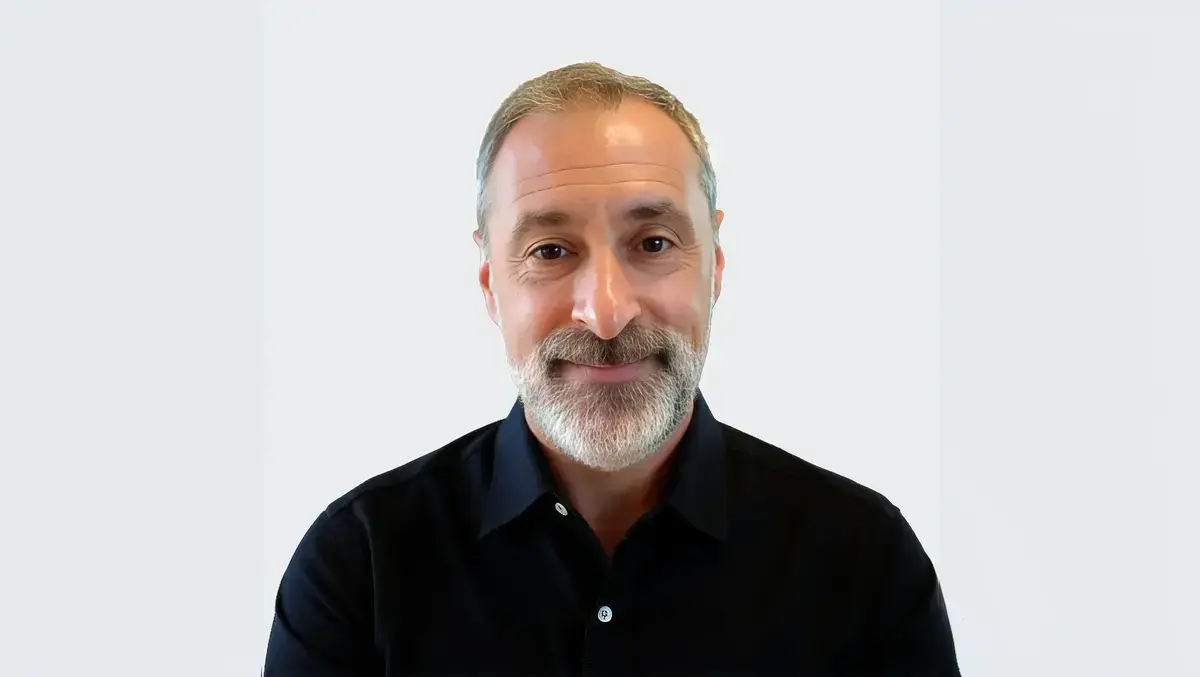
"AI is compressing the time between initial access and business impact, while security leaders remain accountable for the decisions made under that pressure," said Toby Weiss, Chief Executive Officer at Securonix.
"Securonix Advanced Behavioural Analytics helps analysts identify meaningful behavioral change earlier and gives them clear control over how AI supports the response. Consequential response actions remain subject to human approval," Weiss said.
The company also used the launch to underline demand for AI oversight in cyber operations. It cited research based on a survey of 1,000 cybersecurity professionals globally, which found broad support for automation provided it sits within defined approval boundaries.
Among the findings, 96% of respondents said cybersecurity automation is important to their organisation, 49% said they use AI in behavioural analytics with human approval, and 99.6% said their organisation had increased its budget for AI in cybersecurity automation during the past year. Securonix said the results suggest spending has moved beyond experimentation, while trust, governance and human accountability remain live issues for buyers.
Customer view
The release included support from managed security services provider Acora, whose security leadership highlighted the challenge of distinguishing real threats from ordinary activity in fast-changing cloud environments.
"In a managed SOC, the hardest part isn't writing detection rules. It's understanding each customer's environment well enough to separate real threats from normal activity. That becomes even harder in cloud and Infrastructure-as-Code environments, where workloads appear and disappear and identities constantly change," said Darren Humphries, Group CISO at Acora.
"Securonix Threat Analytics builds that behavioral baseline automatically, then uses risk scoring and evidence boards to show our analysts what matters and why. For Acora's customers, that means fewer false positives, faster investigations and quicker containment, without losing the customer context that makes detection effective," Humphries said.
AI governance
Alongside the product launch, Securonix said it has achieved ISO/IEC 42001:2023 certification, which it described as the first AI management system standard. The certification covers the management system used to govern AI across the Securonix product portfolio, including ThreatQ, and followed an external audit with no major findings.
For customers, the certification is likely to matter in procurement and governance reviews as organisations face closer scrutiny over how AI tools are controlled, documented and supervised. Securonix said the standard provides independent validation of accountability, AI risk management and human oversight.
The announcement reflects a broader shift in cybersecurity spending as vendors adapt products for environments where AI systems are not only used by defenders but are also becoming part of the infrastructure attackers may seek to manipulate. In that setting, the distinction between legitimate activity and harmful behaviour is becoming harder to define through static rules alone.
Securonix's position is that behavioural analysis, tied to approval controls and audit trails, will become more important as AI systems take on a larger role in enterprise operations. Its survey figures point to an industry willing to spend more on AI in cybersecurity, while still expecting human accountability to remain in place.