

Ransomware shifts to data corruption, Index Engines says
Wed, 14th Oct 2026 (Yesterday)
Index Engines has published research showing that ransomware strains are increasingly using data-corruption methods that do not rely on full encryption. Its analysis of 1,064 strains found directory-entry destruction in 47.8% of samples.
The findings point to a shift in how ransomware damages data. Attackers are targeting the structures that make files usable while avoiding some of the signs security teams have traditionally used to identify corruption.
According to the research, only 18.3% of the strains analysed used full encryption. The larger share using directory-entry destruction suggests many attacks now aim to make data unreliable or unusable without necessarily changing obvious file characteristics.
Some variants preserved file extensions and timestamps, maintained low entropy, encrypted slowly, or altered only selected parts of files. These methods can make compromised data appear normal in surface-level scans.
The study also examined how quickly destructive activity can spread. Lab testing found a median attack rate of about 97,321 files corrupted per hour, with ransomware reaching 10,000 files in roughly six minutes.
That pace narrows the time available for incident response teams to detect an attack, escalate it, and decide which data can be restored safely. The research argues that the central issue in recovery is no longer only whether a backup exists, but whether the data within it can be trusted.
Detection methods
In a controlled environment, the lab detonated the samples to observe behavioural patterns. It found that newer strains suppress familiar indicators of corruption, such as changed extensions, spikes in entropy, altered timestamps, and sudden bursts of encryption activity.
The research also found polymorphism in 64.7% of analysed samples. In those cases, the ransomware kept its functional code intact while regenerating its file signature between builds, limiting the usefulness of signature-based detection tools.
At the data layer, the lab documented partial encryption, preserved or falsified timestamps, and low-entropy corruption. These approaches reduce the visible footprint of an attack and complicate efforts to identify damaged files quickly.
One finding concerns the role of artificial intelligence in current ransomware campaigns. None of the 1,064 strains analysed showed AI making choices about data at the destructive payload stage, although the research cited broader industry work suggesting AI is appearing earlier in the attack chain, including reconnaissance and lateral movement.
Recovery question
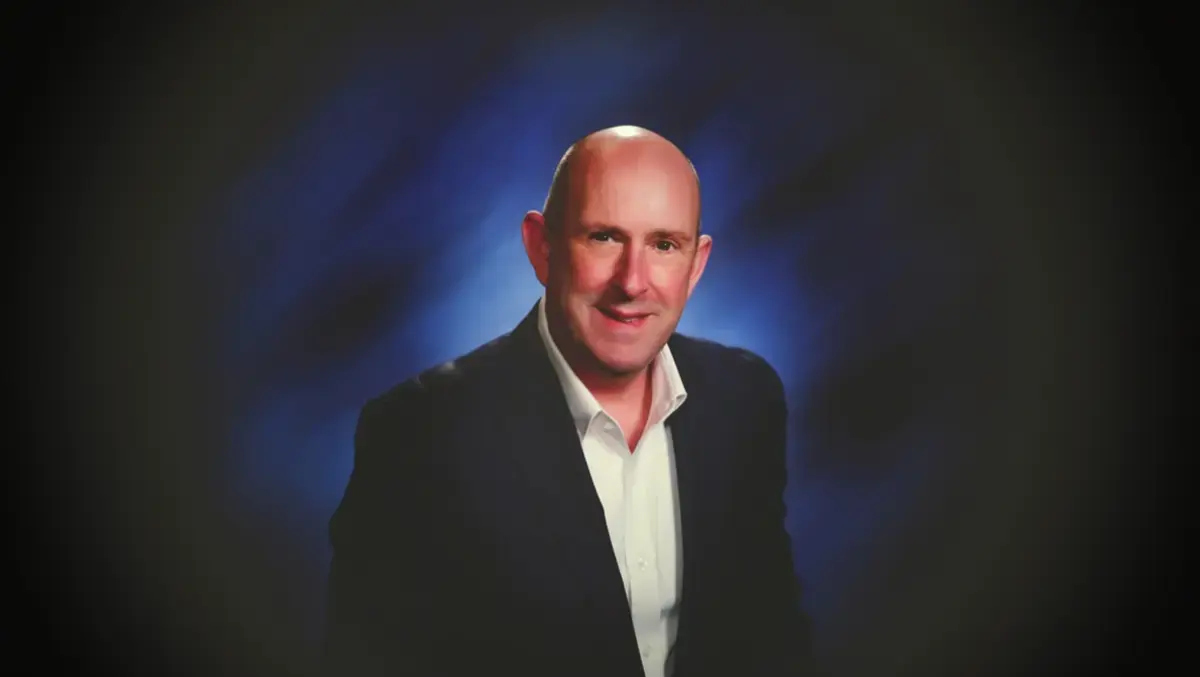
Jim McGann, Chief Marketing Officer at Index Engines, said the changing methods pose a direct challenge for recovery planning.
"Bad actors know what scanning tools look for, and the variants we detonated this year are built to hide it," McGann said.
He pointed to one example from the lab's work.
"Encoder is the clearest example. It destroyed files while leaving their names, sizes, timestamps, and entropy unchanged. A surface scan would report that data as clean. CyberSense caught it by analyzing the content and structure of each file. The Research Lab exists to find techniques like this early and build them into the model our customers rely on for recovery," McGann said.
The purpose of the analysis is to improve the company's models for detecting corruption that may not be visible through standard scanning methods. The findings also suggest organisations should examine whether their recovery processes test data integrity rather than assume files that look normal are fit for restoration.
McGann said the speed of modern attacks leaves little time for traditional response procedures.
"In our detonations, ransomware reached 10,000 files in about six minutes, which is faster than most incident response escalation paths. By the time a team moves to recovery, the question is which copy of the data can be trusted. CyberSense answers it with a forensic account of what was affected and pinpoints clean data to restore from," McGann said.