
Synology urges local control of surveillance video
Tue, 27th Oct 2026 (Today)
Synology has set out its case for keeping surveillance data under customer control rather than relying on cloud-based systems, arguing that rapid advances in artificial intelligence have increased the risks of external access to sensitive video footage.
The storage and surveillance supplier said organisations should process more surveillance data on local devices and keep encryption keys in-house when cloud services are used. It argued that the combination of internet-connected cameras, biometric analysis and opaque AI models has created new concerns for security teams responsible for physical security data.
Synology said many cloud surveillance platforms route raw video across public networks to vendor-managed servers, where the provider controls decryption. It argued that this leaves customers exposed if a provider is misconfigured, suffers an insider threat or uses stored footage to train proprietary AI systems.
The company framed the issue as one of data sovereignty rather than a simple choice between on-site hardware and remote storage. It said organisations need clear visibility over where footage is held, where analytics are run and whether data crosses network or jurisdictional boundaries.
Architecture shift
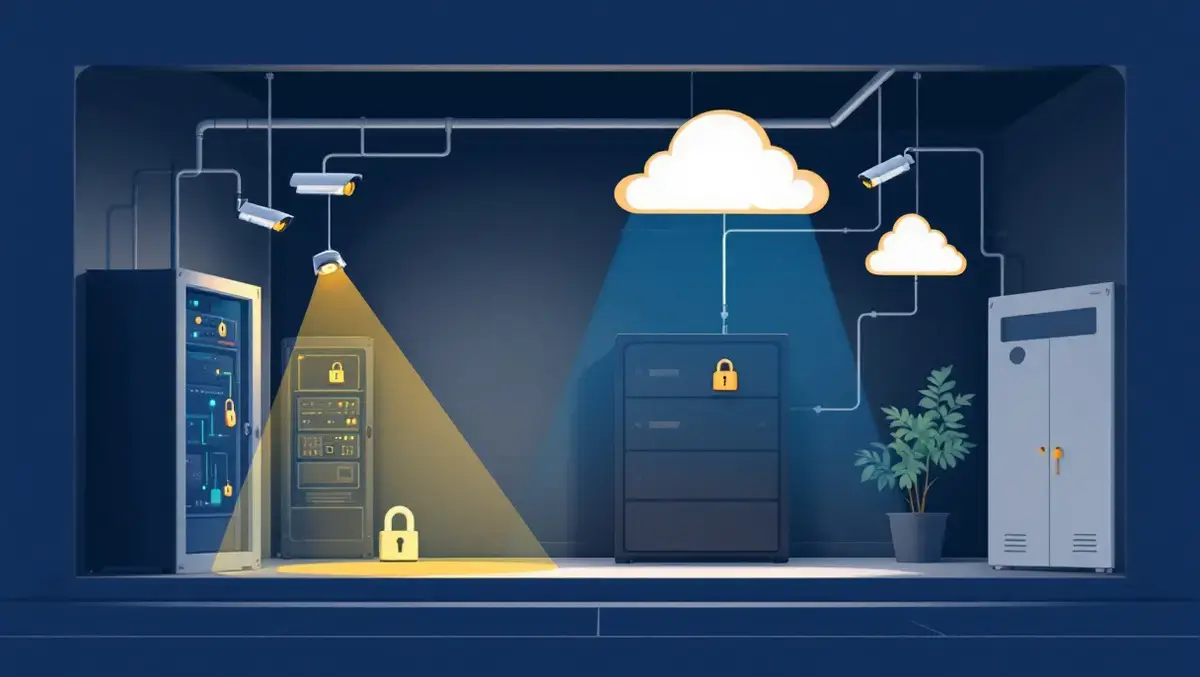
Synology said modern surveillance deployments should be built around an edge-first model. Under that approach, tasks such as facial detection, vehicle tracking and behavioural alerts are handled on smart cameras or on-premises appliances, while only selected metadata is sent for remote alerts or management.
It said this model should be paired with a zero-knowledge cloud structure when remote storage or multi-site oversight is needed. In practice, that means footage is encrypted before leaving the customer environment, and the customer retains sole possession of the keys needed to decrypt it.
Synology also set out four principles it said should govern surveillance design: data residence and transparency; granular access controls and accountability; end-to-end encryption with customer-held keys; and local isolation of AI analytics.
Under its proposed framework, access to live and archived footage would be restricted through role-based permissions and multi-factor authentication. The company also pointed to visible or embedded watermarks to help trace exported or shared video back to its source.
Product tie-in
Synology used the argument to position its own surveillance portfolio, which includes Surveillance Station for on-premises deployments and Surveillance365 for video surveillance as a service. It said the range spans cameras, local AI storage appliances and cloud management software designed to work together under a single encryption model.
The company cited its BC800Z camera as an example of edge processing for licence plate recognition events. For sites requiring heavier local retention and analysis, it pointed to the DVA7400 rackmount system as an on-premises option.
Where footage is backed up or managed through Surveillance365, access is governed through what Synology calls a C2 Encryption Key. It said the design prevents even Synology from viewing customer footage without the key.
Cody Hall, Product Manager, Synology America, said: "We are living through an unprecedented acceleration in artificial intelligence. From Rogue Agents, closed proprietary AI models and the race toward Recursive Self-Improvement and the horizon of Artificial General Intelligence (AGI), we now operate largely within a fog of limited transparency and uncertainty."
Hall set out the company's view of the exposure created by surveillance systems connected to external networks. "Yet, inside those customer firewalls, physical surveillance systems are capturing increasingly intimate data about our daily lives-tracking employee habits, mapping customer behavior, tracing visitor movements, cataloging faces and vehicle license plates in real time. The collision of these two forces creates a profound risk. When smart surveillance systems are tied blindly to cloud infrastructures and opaque external networks, sensitive video data is left exposed to the storm outside. As AI outpaces human policy, security leaders face a new reality: you know what your cameras are watching, but unregulated AI demands we finally ask who is watching your cameras," Hall said.
Wider concern
The intervention reflects a broader debate in the security and IT sectors over where sensitive operational data should be processed and who should control access to it. Video surveillance systems increasingly combine storage, analytics and remote administration, while AI tools are widening the scope for automated identification, pattern analysis and data reuse.
This has focused more attention on how footage is encrypted in transit and at rest, whether biometric analysis runs locally or in the cloud, and whether a supplier can access customer archives. For buyers in regulated sectors, or those with strict internal data-handling rules, architectural choices can affect compliance, audit trails and operational risk.
Hall said: "Because every request to view or retrieve footage through our services must first clear the C2 Encryption Key, your operational footage stays out of reach of anyone without the key, including Synology. We provide the infrastructure; you hold the key that decides who gets in."