Penetration testing stories
Demand for sovereign AI compute has forced the Gagarin site to expand within weeks, with capacity set to rise to 5MW by year-end.
Vendor reviews could be cut from days to minutes as the new AI tool centralises evidence and automates lower-risk approvals.
Attackers are already using AI to exploit flaws faster than many organisations can detect them, Five Eyes agencies warned.
The tie-up gives NCC Group early access to GPT-5.5-Cyber, as OpenAI seeks trusted testers for defensive uses of its cyber tools.
Organisations risk missed exposures as cloud, APIs and AI systems change far faster than annual security checks can keep up.
Customers may see clearer safeguards as cyber security firms adopt AI, with NCC Group joining a charter setting standards for oversight and transparency.
Security teams are being offered new tools to track shadow AI and block prompt injection as enterprises rush to deploy agents and models.
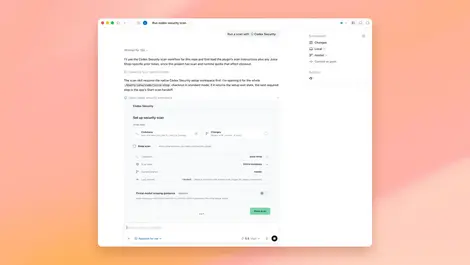
Enterprise security teams gain a new AI-assisted way to spot exploitable code flaws, as IBM widens its cyber work with OpenAI.
The move aims to help defenders turn faster vulnerability discovery into working fixes, as OpenAI broadens access to its cyber tools and partners.
A single phishing email can now compromise identities, bypass multifactor authentication and hit endpoints within five minutes, Barracuda said.
A financial services cloud was taken over in seconds in a test, highlighting how approved permissions can still let attackers reach full AWS control.
Enterprise customers face growing risks as autonomous software gains access to internal systems, prompting fresh demand for agent security tools.
False negatives from automated scanning tools are fuelling a shift towards human-led AI security testing across large organisations.
The certifications may help reassure UK customers and public-sector buyers as cyber breaches remain widespread and scrutiny of suppliers intensifies.
Despite reported gains, fewer than one in four UK organisations trust their cyber defences to withstand a major incident, a survey found.
Researchers can now earn up to USD $6,000 for exposing flaws in Agoda's core web services, APIs and mobile app via HackerOne.
The extension gives Rugby Australia two more years of protection against cyber threats as sporting bodies face rising risks to data and match-day systems.
Continuous attack testing aims to help customers spot exploitable gaps before criminals do, including misconfigurations hiding outside core systems.
Users seeking help with sleep, stress and other everyday issues are driving early uptake of Groov's AI support in New Zealand.
Exploited software flaws are now overtaking stolen passwords as the main breach route, sharpening pressure on security teams to patch faster.